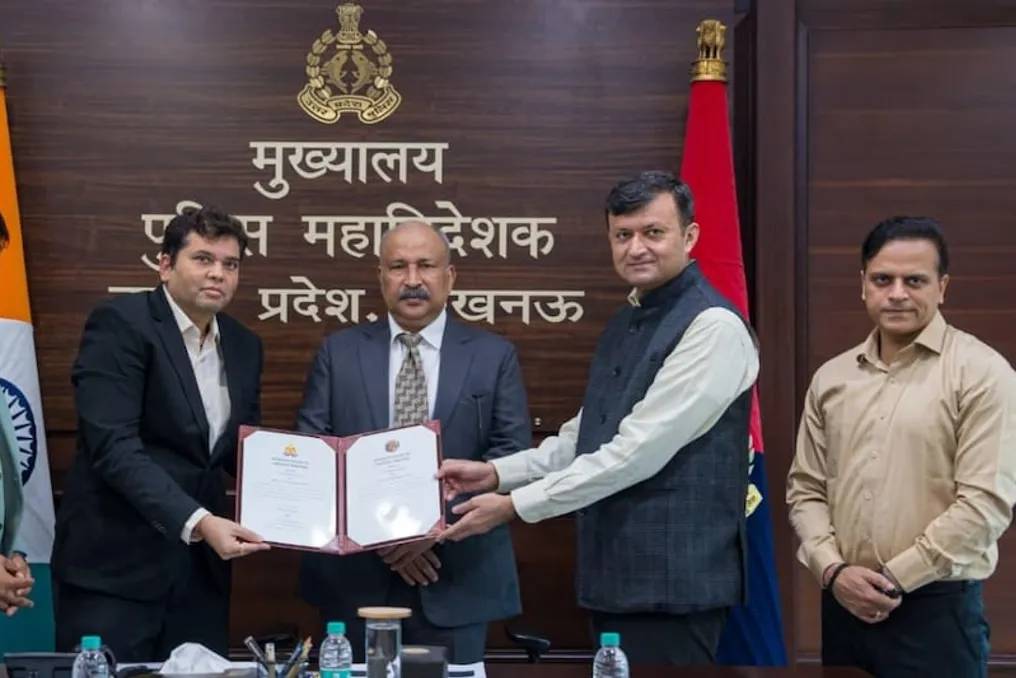
UP Police signs agreements with three institutions to implement AI and cybersecurity
Read more
Aaj Tak
www.aajtak.in

UP Police signs agreements with three institutions to implement AI and cybersecurity

Three major agreements have been signed to enhance the technological capabilities of the Uttar Pradesh police. The UP Police signed Memorandums of Understanding (MoUs) with IIT Kanpur, Digital India Corporation, and Protean eGov Technologies.

The objective of these agreements is to expand the use of Artificial Intelligence (AI) in police operations, improve cybercrime investigation, and ensure the security of digital systems. Furthermore, work will be conducted on directing forensic investigations using digital forensics, data protection, and modern technologies.

Under the leadership of Chief Minister Yogi Adityanath, the process of technical modernization of the UP police is accelerating. The main focus is on equipping law enforcement agencies with modern technologies, increasing the use of digital tools in crime investigation, and providing citizens with higher quality services. Police Director Rajiv Krishna has included technical modernization and innovation among ten police priorities.

As part of this initiative, the police have begun collaborating with various technical institutions and companies to develop and implement new technologies into the law enforcement system.

The agreement with IIT Kanpur provides for joint research and technical cooperation in the fields of cybersecurity, cyber forensics, and artificial intelligence. This partnership will involve assessing the security of UP police's digital systems and identifying potential cyber threats. Modern expertise and technologies will be used to protect police systems from cyberattacks.

It is also planned to enhance technical capacity in crime investigation, analysis of digital evidence, and cases related to cybercrime.

The MoU with Digital India Corporation aims to update the digital services and IT systems of the UP police. Within this partnership, attention will be paid to making the police's online platforms and digital services more efficient, convenient, and technologically advanced. This will help simplify citizen access to police services and improve digital capabilities.

The technical changes will contribute to making police operations simpler, faster, and more citizen-oriented.

The agreement with Protean eGov Technologies will ensure the development of mechanisms for secure data exchange between various digital systems of the UP police. The focus will be on digital identification, authentication, data protection, and integration of different technical platforms. Ensuring secure and orderly data exchange between different systems will strengthen the police's digital activities. The goal of this initiative is to make digital services more reliable and establish better coordination between technical systems.

Bogandan Swarup, Deputy Director of Technical Services, signed all three agreements on behalf of the UP Police. Aashish Tiwari, Director of Technical Services, also played an important role in this initiative. These agreements will be implemented in phases to advance the technical modernization of the police. It is planned to integrate technical expertise, research, and modern digital solutions into police work.

The goal of this UP police initiative is to make the law enforcement system safer, more transparent, and technologically advanced. Increased use of technologies in areas such as AI, cybersecurity, digital forensics, and secure data exchange will help improve the ability to investigate crimes and analyze digital evidence. Emphasis will also be placed on the easy accessibility of police digital services for citizens. After all three MoUs come into effect, the work will focus on strengthening citizen-centric policing by connecting the UP police to modern technologies.
Similar stories

Artificial intelligence accelerates cyberattacks and increases the number of incidents in companies
Read more
olhardigital.com.br

Artificial intelligence accelerates cyberattacks and increases the number of incidents in companies

Progress in artificial intelligence (AI) coincides with a rise in cyber incidents, according to data from the insurance company Marsh. This technology accelerates the pace and scale of attacks, creating new problems for both companies and insurance organizations.

In the last two weeks of October, Marsh clients reported 105 cyber incidents. This volume is more than double the 48 cases registered in the last two weeks of May.

In an interview with Reuters this week, Meredith Schnur, who is responsible for Marsh Risk's cyber risk practice in the US and Canada, noted signs that attackers are using AI tools to find vulnerabilities in systems.

"There are signs that attackers are using AI-based and agent tools to identify vulnerabilities. So I would say that we can attribute a significant number of these incidents to AI," stated the head.

Among the exploited weaknesses are unpatched software, open systems, and weak identification mechanisms. Artificial intelligence allows criminals to find and exploit these vulnerabilities much faster.

The popularization of such tools also facilitates the expansion of criminal activity at lower costs, increasing the potential number of targets. According to Schnur, this trend, combined with the slow response of organizations to attacks and incidents, explains a significant part of the recent increase in registrations.

"AI itself is not a threat; it is an amplification of risk in all areas," emphasized the head.

The increased frequency of attacks should also stimulate the digital risk insurance market. According to GlobalData forecasts, cyber insurance premiums—the amounts companies pay for policies—are expected to grow globally faster over the next two years, following the increased frequency of attacks.

The consulting firm predicts that the global market will grow by 6.9% in 2026, reaching USD 16.6 billion (approximately BRL 94.62 billion). In 2027, growth is expected to reach 10%, increasing the volume to USD 18.3 billion (approximately BRL 104.31 billion).

New data laws stimulate demand for cybersecurity specialists in companies
Read more
www.aajtak.in

New data laws stimulate demand for cybersecurity specialists in companies

Significant opportunities are expected in the field of cybersecurity in the coming years. India is preparing for the implementation of a strict personal data protection law—the Digital Personal Data Protection (DPDP)—which is set to take effect on May 13, 2027. Consequently, companies are beginning to prepare for the recruitment of security experts and managed security services to protect private data.

According to a new technical document from K7 Cyber Security titled 'Transforming DPDP Compliance into Security Capability,' companies can no longer rely solely on basic, paper-based security policies. They must demonstrate that their security systems are actually functioning. This is expected to increase the demand for qualified cybersecurity professionals.

Companies will require professionals capable of controlling data access, investigating suspicious activity, and managing a Security Operations Center (SOC). As the May 2027 deadline approaches, companies will have to increase their investments in cybersecurity.

The primary driver for strengthening corporate security systems is the threat of heavy fines. Under the new DPDP law, if a company fails to implement adequate protective measures, it may be fined up to 250 million rupees. Furthermore, if a company does not provide proper information following a data breach, it faces an additional fine of up to 200 million rupees.

The regulations require the company to immediately notify affected individuals and the Data Protection Board about the theft of user data. After discovering a data breach, the company must provide a detailed report within exactly 72 hours, although this period can be extended with special permission.

It is no longer sufficient to simply install general software and forget about it. In accordance with Rule 6 of the new framework, companies are obligated to implement serious technical security measures. These include data encryption, masking of sensitive information, strict data access control, and developing a backup plan to ensure business continuity after a cyberattack.

The K7 report indicates that companies must ensure the security of data stored in their applications, cloud services, office devices, and with third-party vendors. If a company engages an external vendor to process data and a leak occurs, the legal liability rests with the main company, and it cannot shift this responsibility to a third party.

To meet these needs, companies will invest in managed SOC services. The report mentions the use of an agent-based SOC, where Artificial Intelligence (AI) agents will perform routine tasks daily. These tasks include collecting incident timelines, checking old records, and closing low-risk security alerts.

However, according to the technical document, AI will not replace human jobs. Control over critical decisions, such as handling legal matters, communicating with regulators, and taking serious action during a major cyberattack, must remain with human experts.

Given the deadline of May 13, 2027, companies must either build their own strong cybersecurity teams or utilize the services of external expert agencies. Protecting private data will cease to be merely a legal necessity and could become one of the largest job-creating industries in the digital sector.

Artificial intelligence has turned cybersecurity into an arms race that companies cannot ignore
Read more
techcentral.co.za

Artificial intelligence has turned cybersecurity into an arms race that companies cannot ignore

Cyber threats, which are becoming increasingly sophisticated thanks to artificial intelligence, are forcing companies worldwide to respond to a wave of attacks. These attacks range from hacking refrigerators in supermarkets to large-scale cryptocurrency theft on the Binance platform and issues with widely used web software.

This surge in threats places a significant burden on IT departments, where employees are forced to work around the clock to eliminate software vulnerabilities. In response, some companies are beginning to increase investments in AI-based security tools to manage the increased workload.

A recent cyberattack on European supermarkets highlighted the urgency of the problem. It was the second such attack in three weeks, when hackers raised the temperature in refrigerators and freezers, forcing retailers to discard millions of dollars worth of products.

Marnie Wilking, Chief Security Officer at the service platform Booking.com, noted that the situation is an 'endless game of cat and mouse with very high stakes.' She added that even after blocking one route, attackers quickly move to the next, and hundreds of company engineers are now dedicated to developing AI-based defense systems.

According to the international registry of disclosed vulnerabilities, Common Vulnerabilities and Exposures, nearly 37,000 software or computer system vulnerabilities were registered in the third quarter of 2026, triple the figure from the previous year.

Marcus Noga, CTO of the German hosting company Ionos, which serves seven million customers, stated that events of this magnitude occur weekly or even every few days, whereas previously they happened monthly.

Ionos changed its security methods after a sharp rise in vulnerabilities in July, implementing AI-based monitoring systems to detect threats and using AI-supported tools to patch its systems around the clock.

Cyber threats drive up defense spending

Binance, which was hit by hackers who stole $6.3 billion in cryptocurrency, announced plans to increase investment in AI-enhanced detection systems. Port of Rotterdam is working on creating an AI-based 'cyber shield,' and Siemens is testing advanced AI models for defensive security.

The Dutch food retailer Ahold Delhaize, which manages Stop & Shop and Giant Food chains in the US, suffered two hacks in the last month. The first, in mid-October, led to a loss of over 200 million euros in revenue and triggered a profit warning.

As a result of this incident, Ahold shut down its websites and applications for a week after discovering the intrusion. This week, some of its stores in Belgium and Luxembourg were also victims of refrigerator cyberattacks across a dozen European countries.

CFO Jolanda Poots-Bijl stated that the company is adapting to the new reality, noting that small businesses are particularly vulnerable. She emphasized that AI is a defensive tool that helps detect threats and recover much faster than previously possible.

McKinsey predicts that the global market for third-party cybersecurity products and services will grow from $223 billion in 2025 to $346 billion by 2029.

AI tools help researchers reproduce hacks

Refrigerator attacks demonstrate how AI forces companies to promptly fix vulnerabilities once discovered, according to Sean Tufts, Field Technical Director at cybersecurity firm Claroty. Claroty published a study in August, several months before the attacks began, detailing weaknesses in refrigeration equipment controllers.

Following the first wave of attacks on stores in France on October 11, Claroty researchers used publicly available AI tools to reproduce these flaws and capture a test device, thereby highlighting the risk of further attacks. Tufts reported that they managed to recreate the attack for only $6 and 28 minutes.

The disclosure of two vulnerabilities in the PHP programming language, found using AI, on October 21, which underpins many websites, prompted governments and companies from Tokyo to Helsinki to temporarily take their sites offline as a precaution. In South Africa, the presidential administration took its site offline two days later 'as a preventive measure in response to a global cybersecurity event,' although it did not name PHP.

American internet infrastructure firm Cloudflare reported that attempts to exploit PHP vulnerabilities rose from thousands to millions within hours of their disclosure. The company noted that errors found with AI could lead to more future outages.

Kraft Heinz CEO Steve Kehlen stated that the threat is real and growing, emphasizing that cybersecurity is 'more important today than yesterday, and will be even more important tomorrow.' Holcim CFO Stephen Kindler supported this view. The Swiss building materials manufacturer took its website offline around October 21st at 9:30 PM to apply PHP patches and restored service by midnight. He noted: 'We need to get smarter. Both sides are well-equipped. Both sides use AI, and this race continues.'

Popular