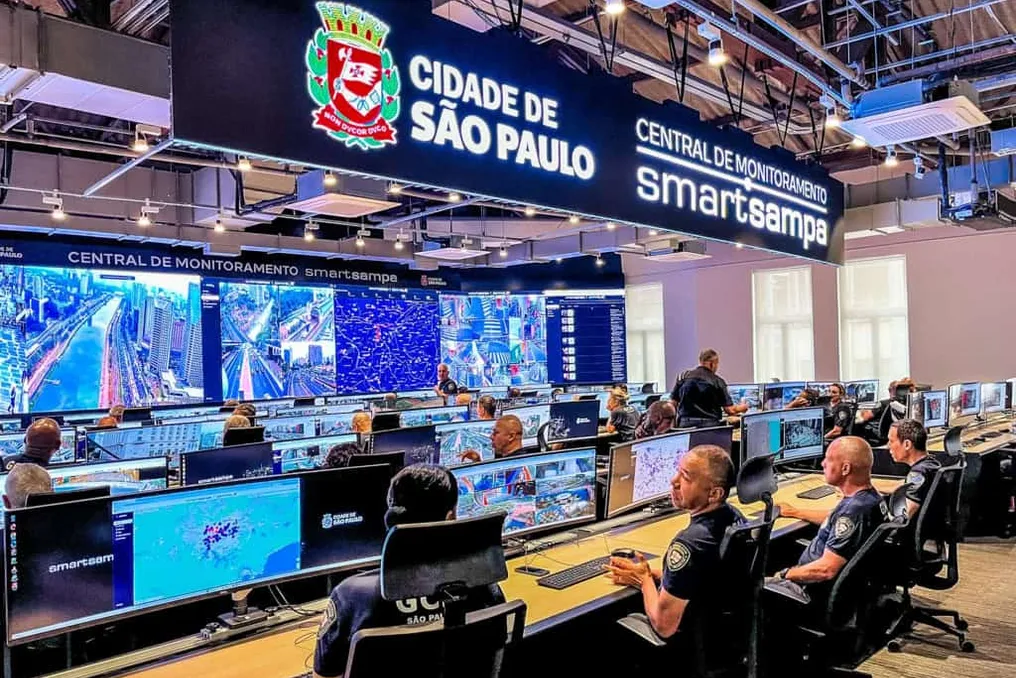
A vulnerability in Smart Sampa, the surveillance system operated by the São Paulo City Hall, allowed unauthorized access to over 58 thousand cameras. This exposure occurred after confidential data was available on the internet for approximately eleven months, affecting critical locations such as hospitals, schools, and daycare centers.
According to UOL, the compromised material included access credentials and information related to security agents. Although the city hall attributed the leak to a specific server and denied any failure in the program's security protocols, the public repository contained 181 pairs of authorized user logins and passwords, data from over six thousand security agents, in addition to instructions on replicating the system on mobile and computer devices.
With this obtained information, journalists were able to view images of vehicles and people circulating through the streets of the capital, as well as access cameras installed in centers for drug addicts, daycare centers, and hospitals. Furthermore, it was possible to access the Sentinelx platform, the technology provider, without needing to go through the two-factor authentication process.
After being notified, the city hall implemented security reinforcements. An additional investigation revealed interfaces that, according to a technology expert interviewed by UOL, could allow data transmission without adequate verification of the sender's identity. The risks went beyond images, as the credentials also provided access to records and personal information contained in the database.
Rafael Alcadipani, a professor at Fundação Getulio Vargas (FGV) and public safety specialist, warned that access to the images could expose the movement of security equipment and authorities, stating that such a state structure could be used by crimes against the State itself. Pedro Saliba, a researcher at Data Privacy Brasil, also voiced his criticism, classifying the incident as a 'very serious failure in terms of privacy and surveillance.'
Saliba emphasized that monitoring systems must adhere to the principles of the General Data Protection Law (LGPD), including transparency, necessity, purpose, and security in handling information. Data protection issues are compounded by the lack of clarity regarding the use of facial recognition. The City Hall reported that it does not have access to the source code, artificial intelligence models, or the databases used to train the algorithms, and that it does not conduct independent audits of these models.
Another point of attention raised by the records of approaches is as follows: between November 2024 and May 2026, 268 individuals were taken to police stations following facial recognition alerts but were later released. Of these cases, 75 presented identification inconsistencies, 181 had outdated warrants, and 12 had registration problems.
In an official statement, the São Paulo City Hall alleged that the leak was illegally caused by a server, which was identified, removed, and is under investigation by the Metropolitan Civil Guard's Inspectorate. The administration refuted the idea of weaknesses in the security mechanisms and contested the classification of the event as a platform failure. The city hall also detailed that it reinforced protection by implementing exclusive passwords, two-step authentication, and SMS validation for creating new passwords, mentioning the oversight of the Municipal Court of Accounts and the hiring of specialized consulting in governance and privacy.
Smart Sampa uses facial recognition to locate missing or wanted persons and to identify stolen or stolen vehicles. However, the exposure of the data calls into question both the access controls and the safeguarding of the information collected by this extensive urban surveillance network.